Cybersecurity for organisations that are not security companies
Threats keep changing. What protects a normal organisation has changed much less.
Logic Networks helps businesses, charities and schools across London and the rest of the UK reduce the risk they actually face. That starts with accounts, devices, updates and backups, in that order, because that is where the great majority of incidents begin.
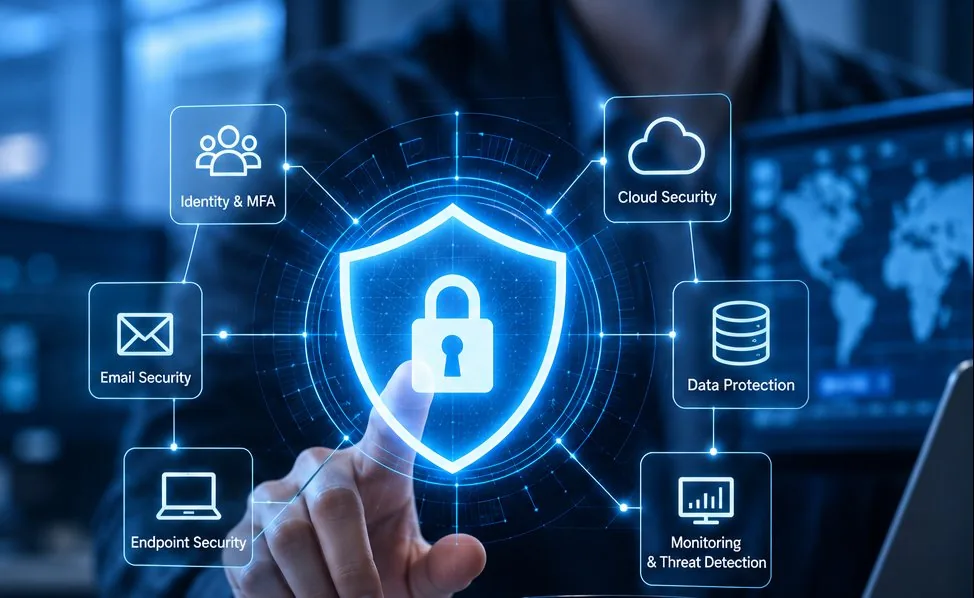
We look across identities, devices, email, cloud services, networks, applications, data, backup and the habits of the people using all of it.
The work is deliberately unexciting. A monitoring tool on an environment where anybody can sign in with a password alone is money spent in the wrong place.
The attacks that reach small organisations are rarely clever.
They use a password bought in bulk, an update that was available and not applied, or a message that asks somebody to change a bank account. All three are preventable with work that costs very little.
- A second check at sign in, including the administrators
- Updates applied and evidenced, not just enabled
- A backup you have restored from, kept out of reach
- One written rule for changing payment details
What is included
Seven layers, worked through in order of what removes the most risk first.
We do not recommend starting at the bottom of this list. Organisations that buy monitoring before they have fixed sign in tend to be the ones monitoring an incident they could have prevented.
Identities and access
A stolen password should not be enough.
Multi factor authentication on every account, administrator rights held by as few people as possible, and a process for joiners and leavers that actually ends access on the right day.
This is the layer with the largest return. In most organisations we review, the administrator accounts are the ones without a second factor, which is the wrong way round.
Devices and endpoints
Every machine accounted for.
Protection on each laptop, desktop and mobile, disk encryption so a lost device is not a data breach, and a way to wipe one remotely.
We also keep a list of which machines exist. An unmanaged laptop that somebody uses for work is the gap that makes the rest of the effort optional.
Email and the human layer
Filtering, plus the rule that catches the careful one.
Filtering removes most of the volume. It will not remove the message that arrives from a supplier’s real address and asks you to update their bank details.
The control that catches that one is a written rule: any change of payment details is confirmed by telephoning a number you already hold, with no exceptions for urgency. We help you write it and make sure the people who pay invoices know it.
Updates and vulnerabilities
Evidence, not intentions.
Operating systems, browsers, the applications people use and the network equipment nobody looks at. Most successful intrusions use a flaw that had a fix available.
What matters is the monthly evidence that machines are on the version you believe they are, including the laptop belonging to the person who never restarts.
Backup and recovery
A copy the attack cannot reach.
Backups are a security control, not only an accident control, because the modern incident encrypts your data rather than stealing it.
That means a copy held where your normal accounts cannot delete it, and a restore that has been tested and dated. An untested backup is a hope.
Networks and boundaries
The edges kept in order.
Firewalls configured rather than installed, guest wireless kept away from your own systems, and remote access built so it can be verified rather than merely opened.
Old rules are the common problem. A firewall accumulates permissions over the years and nobody removes the one added for a supplier who left in 2019.
Review and testing
Finding it before somebody else does.
A periodic look at what has drifted: new accounts, new devices, permissions granted during a busy week and never withdrawn.
We also help with the security questionnaires that clients, insurers and funders now send, and we arrange testing through specialist partners where a client requires an independent test.
How it works
Three ways in, and the first one costs you nothing to decide on.
Security work goes wrong when it is bought as a product before anybody has looked at the environment. So the sensible order is to look, then to fix, then to keep it in order.
Tell us which of the three matches where you are and we will say what the first week would look like.
-
A review
We check the seven layers above against what you have and come back with a list in priority order, with costs. Yours to act on however you like.
-
A piece of work
One defined project: rolling out a second factor, sorting the firewall rules, setting up a backup that can be restored. Scoped, dated, finished.
-
Kept in order
Security handled continuously as part of managed IT, with the reviews and the evidence produced each month.
Who it is for
Almost every organisation now has a reason to do this, and for most of them the reason arrived from outside: a client questionnaire, an insurer’s renewal form, a funder’s condition, or an incident at a company they know.
What differs by sector is what you have to be able to prove, and to whom.
- Businesses asked to answer a client or insurer security questionnaire
- Charities and non profits holding personal data on beneficiaries
- Education organisations with duties towards staff and students
- Organisations that handle money and have been targeted by invoice fraud
- Teams with staff working from home on their own equipment
- Anyone who has just had an incident and wants the honest picture
What we need from you
Security is the area where the organisation has to participate. Three things make the difference.
The third one is the one people underestimate. Controls that staff work around are worse than controls you never installed, because they create a false picture.
Someone who can say yes
A second factor, tighter permissions and device rules all inconvenience somebody. Those decisions need an owner who will not reverse them at the first complaint.
An honest inventory
Every account, every device, every service somebody signed up for. The shadow items are where the gaps are, and nobody is in trouble for naming them.
Willingness to tell staff why
People cooperate with a reason and work around a rule. Ten minutes explaining the invoice fraud rule does more than any product on this page.
What we usually find in the first review
None of these is unusual. Every one of them has been in an organisation that believed it was in reasonable shape.
- Administrator accounts without a second factor
- Accounts still active for people who left months ago
- Administrator rights on ordinary users, granted years ago for one task
- A backup running but never restored from, and reachable from the network it protects
- Firewall rules added for suppliers who no longer exist
- A machine or two that cannot be updated because an old application depends on it
- No written rule for changing a supplier’s bank details
- Staff using personal devices for work with nothing on them
Our steps for working together
Security work is sequenced, because each layer depends on the one before it. This is the order we use and the reason for it.
- Find out what exists Accounts, devices, services, network rules and backups. Not what the documentation says, what is actually there.
- Close the account gaps A second factor everywhere, administrator rights reduced, leavers removed. Cheapest work, largest effect.
- Get updates and devices in order Every machine managed, protected, encrypted and on a current version, with monthly evidence.
- Make the backup trustworthy Held out of reach, restored from once as a test, and dated.
- Tidy the boundaries Firewall rules reviewed, guest wireless separated, remote access rebuilt if it cannot be verified.
- Write the human rules Payment verification, reporting a suspicious message, and what happens when somebody loses a device.
- Review it on a cycle Because every one of the items above drifts back within a year if nobody looks.
How we set priorities
Anything that would let an outsider sign in comes first. Then anything that would stop you recovering. Then anything a client or insurer has asked you to be able to prove. Convenience comes last, and we will say plainly when a request of yours falls into that category.
If something has already happened
Tell us in the first line of your message. The order of work changes: contain the account, look for forwarding rules, establish the window, warn the people who could lose money, and write down what was found. Do not delete the affected account, and do not stay quiet to avoid embarrassment. Both make the outcome worse.
What we will not claim
- No unbreakable protection The aim is to remove the common attacks and to shorten the recovery from the rest.
- No certification you have not earned Where a client asks for a formal standard, we prepare you for the assessment and say clearly what is still outstanding.
- No independent testing pretending to be ours Where a client requires a penetration test, we arrange it through specialist partners and tell you who did it.
- No numbers we cannot show you Any figure in a report comes from your own environment, with the source named.
The questionnaires clients and insurers now send
Security questions have moved from being a formality to being a condition of the contract. Insurers ask them at renewal, larger clients ask them before they place work, and funders ask them before they release money.
The questions repeat. These are the ones that appear on nearly every form, and they are worth being able to answer without a meeting.
- Is multi factor authentication enforced on all accounts, including administrators
- How are software updates applied, and how do you evidence it
- Are backups held separately, and when was the last successful restore
- Are laptops encrypted, and can you wipe one remotely
- How is access removed when somebody leaves
- Do staff receive security awareness training, and how often
- Do you hold a formal security certification, and if not, what do you do instead
- Who do we contact, and how quickly, if there is an incident
We keep the answers for your organisation in one document, updated as things change, so the next form takes an afternoon. Where an answer is currently no, it goes on the order of work above rather than being softened on the form.
What good looks like
You can say, today, how many accounts have a second factor and how many administrators there are. Your last test restore has a date on it. The person who pays invoices knows the payment rule without looking it up. New devices arrive managed. And when a client sends a security questionnaire, answering it takes an afternoon rather than a fortnight.
Related services
Most of the controls on this page are applied through the other services rather than bought separately. That is deliberate: security that lives outside the day to day work is the security that drifts.
Where you already have one of these in place, we work with it rather than replacing it.
- Microsoft 365 for sign in rules, device rules and leavers
- IT support for patching, accounts and the day to day
- Backup and disaster recovery for the copy you recover from
- Devices and endpoints for laptops, mobiles and encryption
- Networks and infrastructure for firewalls and remote access
Articles and news on cybersecurity
Practical notes on the controls that matter, written for organisations that have other work to do.
The first hour after a suspected email compromise
What to do, in order, when you think somebody has got into a mailbox. Written to be followed by whoever is in the office at the time.
Read the articleThe five security controls worth putting in place first
Security spending often starts at the wrong end. These five controls remove the largest share of everyday risk and cost the least.
Read the articleTalk to us about cybersecurity
Tell us what worries you, or send us the questionnaire a client has asked you to complete. We will review what you have and come back with the honest picture and an order of work.
If something is happening right now, say so in the first line.